SOVEREIGN DATA, GOVERNED AI, CUSTOMER CONTROL
Your DataYour AIYour Control
Keep critical information, AI processing, and infrastructure under the control your organization needs. SDS designs and engineers sovereign technology solutions around your business, risk requirements, and future, integrating CPU-first architecture, accelerated AI clusters, resilient microgrid power, zero-trust security, and post-quantum encryption to support secure operations and full operational jurisdiction.
SOVEREIGN COMPUTE. RESILIENT BY DESIGN.
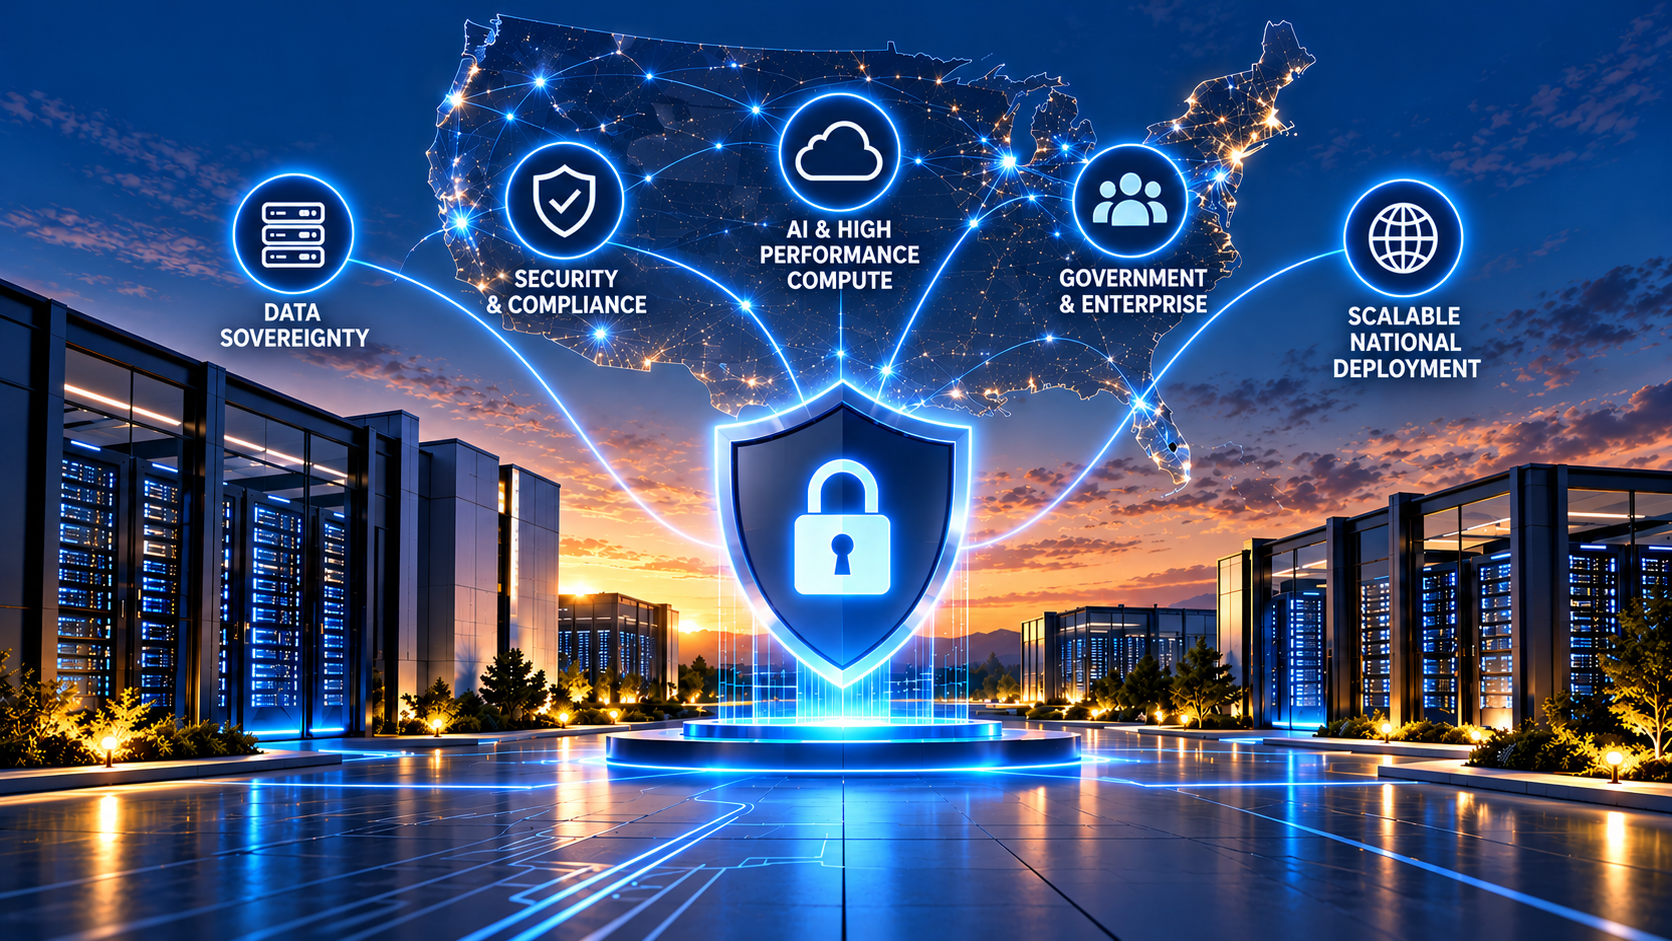
YOUR CONTROL
Keep authority over your information.
Define control over documents, IP, contracts, email, identities, and encryption keys.
YOUR CONTINUITY
Make resilience part of the foundation.
Begin with secure data services, backup, and recovery. Expand energy resilience in phases.
YOUR GROWTH
Scale with purpose.
Deploy across onshore, offshore, remote, and high-risk environments. Expand infrastructure, computing capacity, and power capabilities as operational demands and business requirements evolve.
CONTROL THAT GOES BEYOND LOCATION
Data residency is a starting point. Sovereignty is the architecture.
Sovereignty begins with your information: who can access it, who holds the keys, where it resides, and who has authority over its use.
Documents, intellectual property, contracts, and email belong at the center of the sovereignty conversation. SDS connects customer-defined governance with controlled data services, dedicated compute, and security boundaries. Containerized deployment supports the initial solution; power resilience advances through a phased buildout.
PRIMARY SOLUTIONS | SOVEREIGNTY OVER YOUR INFORMATION
Protect the information that defines your organization.
Start with ownership, access, jurisdiction, and operational control. Design each solution around the customer's governance requirements.
Sovereign data platforms
Controlled storage and data services with defined residency, access policies, key ownership, backup, and recovery requirements.
Documents & organizational knowledge
Govern document repositories, version history, permissions, retention, and the information used by internal knowledge and AI systems.
IP & proprietary information
Establish boundaries for research, designs, source code, trade secrets, models, and other proprietary assets.
Contracts & business records
Define controls for agreements and sensitive records, including authorized access, change history, retention, and audit requirements.
Email & communications
Evaluate mailbox hosting, message storage, routing, encryption, archiving, and administrative access within the required sovereignty boundary.
Customer-defined control
Apply identity, permissions, encryption, audit, and recovery requirements across the information lifecycle.
Hosting location, provider dependencies, administrative access, and migration scope are assessed for each service.
INITIAL DEPLOYMENT | CONTAINERIZED INFRASTRUCTURE
A controlled environment. A modular starting point.
SDS’s initial deployment approach places sovereign data services in containerized infrastructure, using platforms such as Armada and comparable container solutions.
The container houses the computing foundation; SDS defines the service architecture, governance, security, and operating requirements around the customer’s information.
Explore container deployments ↗Customer governance + QFZS™ security + backup and recovery
THE SDS ARCHITECTURE
Start with the workload. Build for the mission.
Data sovereignty sets the requirements. CPU-first compute and selective acceleration support the services deployed within the container.
General-purpose strength. Purpose-built allocation.
CPU-first architecture prioritizes enterprise applications, databases, orchestration, storage services, and workloads that benefit from flexible general-purpose compute.
- Define workload, memory, storage, and network requirements.
- Establish a capable CPU foundation.
- Add acceleration where the workload justifies it.
ZERO TRUST + CRYPTO AGILITY + POST-QUANTUM READINESS
QFZS™ | THE SECURITY AND SOVEREIGNTY FRAMEWORK
Quantum-resistant by design. Federated by architecture.
Quantum-Resistant Federated Zero-Trust Sovereign Secure Systems.
QUANTUM-RESISTANT
Prepare for the next cryptographic era.
Plan for NIST FIPS 203, 204, and 205 implementation and crypto-agile systems.
FEDERATED
Connect without surrendering control.
Design federation around defined trust boundaries.
ZERO TRUST
Verify every interaction.
Identity-based access, least privilege, and segmentation.
SOVEREIGN SECURE SYSTEMS
Keep authority close to the mission.
Define who controls identities, keys, and infrastructure.
Standards inform the design; implementation scope and independent validation are established for each deployment.
POWER RESILIENCE | A PHASED BUILD-OUT
Sovereignty leads. Power resilience grows with it.
Power is a priority. Its buildout follows the deployment plan, site readiness, and validated customer requirements.
Deploy sovereign data services
Establish the container platform, secure data services, backup, and recovery. Engineer the power and cooling needed for the initial deployment.
Add SDS power capabilities
Introduce SDS-branded generation, energy storage, and coordinated controls.
Advance toward Grid N+
Expand local generation and storage toward the SDS doctrine of non-grid primary power.
Critical workloads deserve deliberate infrastructure.
Government & mission systems
Evaluate dedicated infrastructure, jurisdictional requirements, and disconnected operations.
Critical infrastructure
Plan resilient computing for energy, utilities, and operational environments.
Organizational data & private AI
Design governed inference, analytics, and enterprise data services.
The AI ecosystem needs a resilient foundation.
SDS's first priority is sovereignty over organizational information, delivered through containerized infrastructure. Power resilience is a phased expansion of that foundation.
Explore the investor perspective ↗One mission.Your Control.
Sovereign Data Solutions puts sovereignty over organizational data first — including documents, intellectual property, contracts, and email.
Our initial deployment approach uses containerized infrastructure such as Armada and comparable platforms. CPU-first architecture, cybersecurity, and QFZS³ support the primary data services. SDS-branded power capabilities are added through a phased buildout toward Grid N+ resilience.
Clarity before commitment.
START A CONVERSATION
What does sovereignty mean for your mission?
Tell us which data, documents, IP, contracts, or email you need to control. We'll start with your sovereignty requirements and deployment priorities.
325 N SAINT PAUL ST STE 3100
DALLAS, TX 75201